Add fine-grained authorization to an Express.js app
Build an Express.js API for a blogging platform that registers users in Permit.io and allows only users with the Author role to create posts. This tutorial is for Node.js backend developers who want to enforce Permit.io policies from Express route handlers.
When you finish, your Express.js app has two endpoints:
| Endpoint | What it does |
|---|---|
POST /register | Syncs a user to Permit.io and assigns the user the Reader role in the default tenant |
POST /posts | Calls permit.check() and returns 403 unless the user has permission to create a Post |
Prerequisites
- A Permit.io account. See Create a Permit.io account.
- Node.js and npm, to run the Express.js app and install the Permit CLI.
- Docker, to run the policy decision point (PDP) container.
- An Express.js project, or an empty directory where you create one. See the Express installation guide.
1. Configure the policy in Permit
Create the blogging platform policy with the Permit CLI. If your environment already has a policy with a Post resource and an Author role that can create posts, skip to 2. Get your API key.
Install the Permit CLI
The Permit CLI creates policies and runs the PDP from your terminal. Install the CLI with npm:
npm install -g @permitio/cli
Run permit to confirm that the CLI is installed.
Sign in with the Permit CLI
Authenticate the CLI with your Permit.io account:
permit login
The command opens a browser window where you sign in. After you sign in, the CLI uses your default environment. To use a different environment, run permit env select and choose the environment.
Apply the blogging platform template
Permit CLI templates create a policy with predefined resources, roles, and rules. To see the available templates, run permit env template list. The template source files are in the Permit CLI repository.
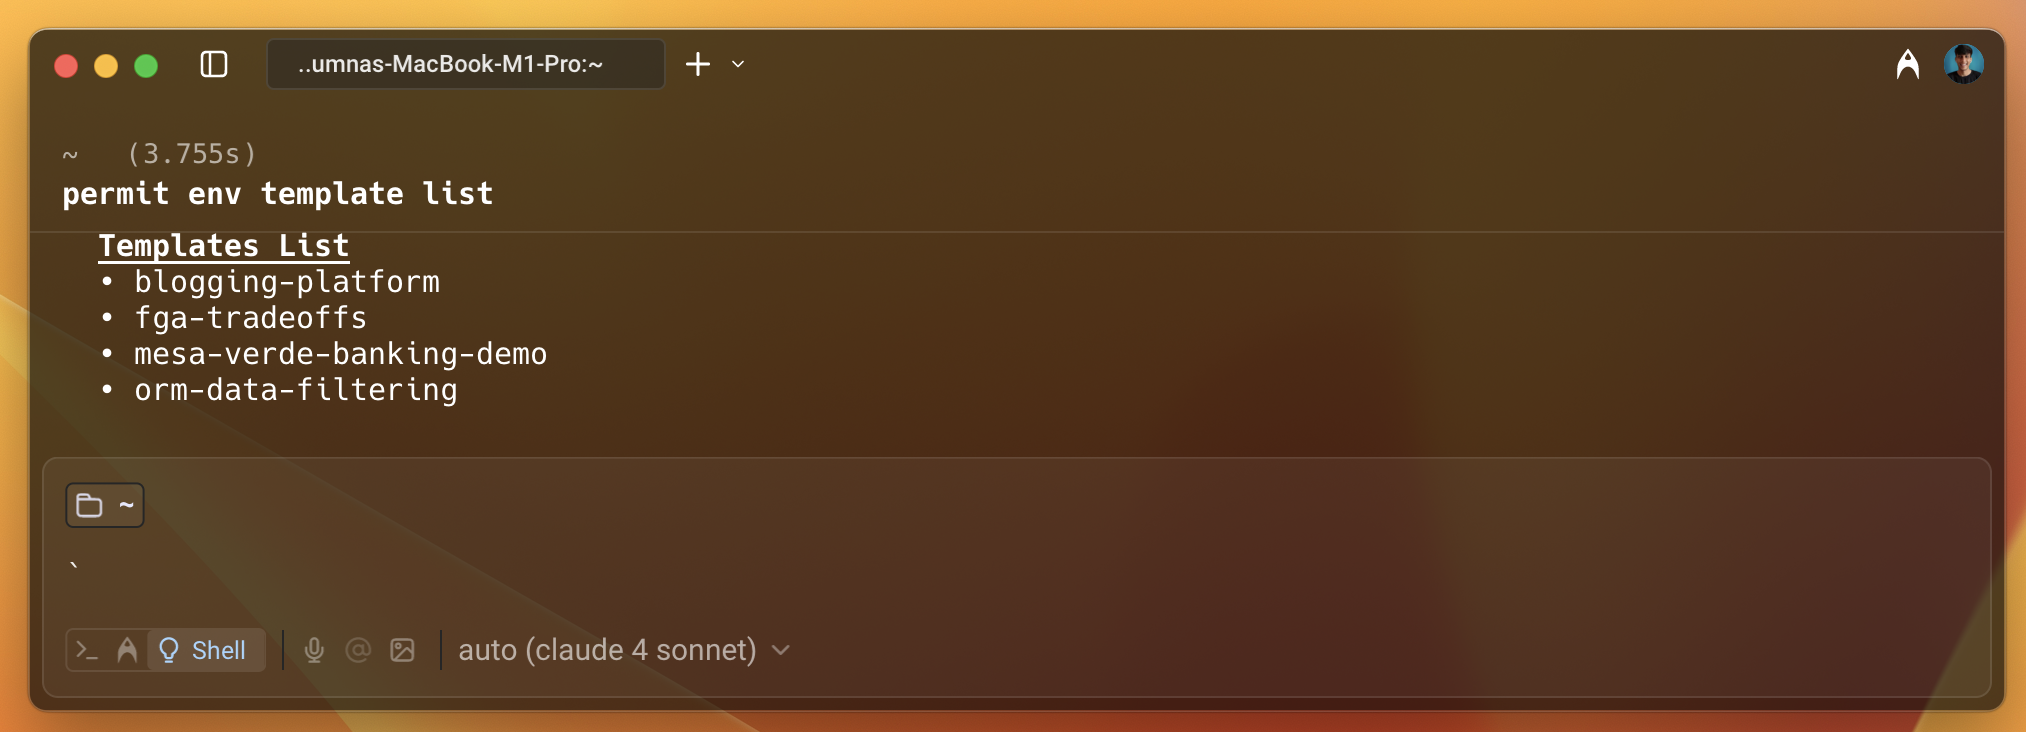
Apply the blogging-platform template to your environment:
permit env template apply --template blogging-platform
The CLI prints a success message when the template is applied.
Review the policy in the Policy Editor
In the Permit dashboard, select your project and open the Policy screen.
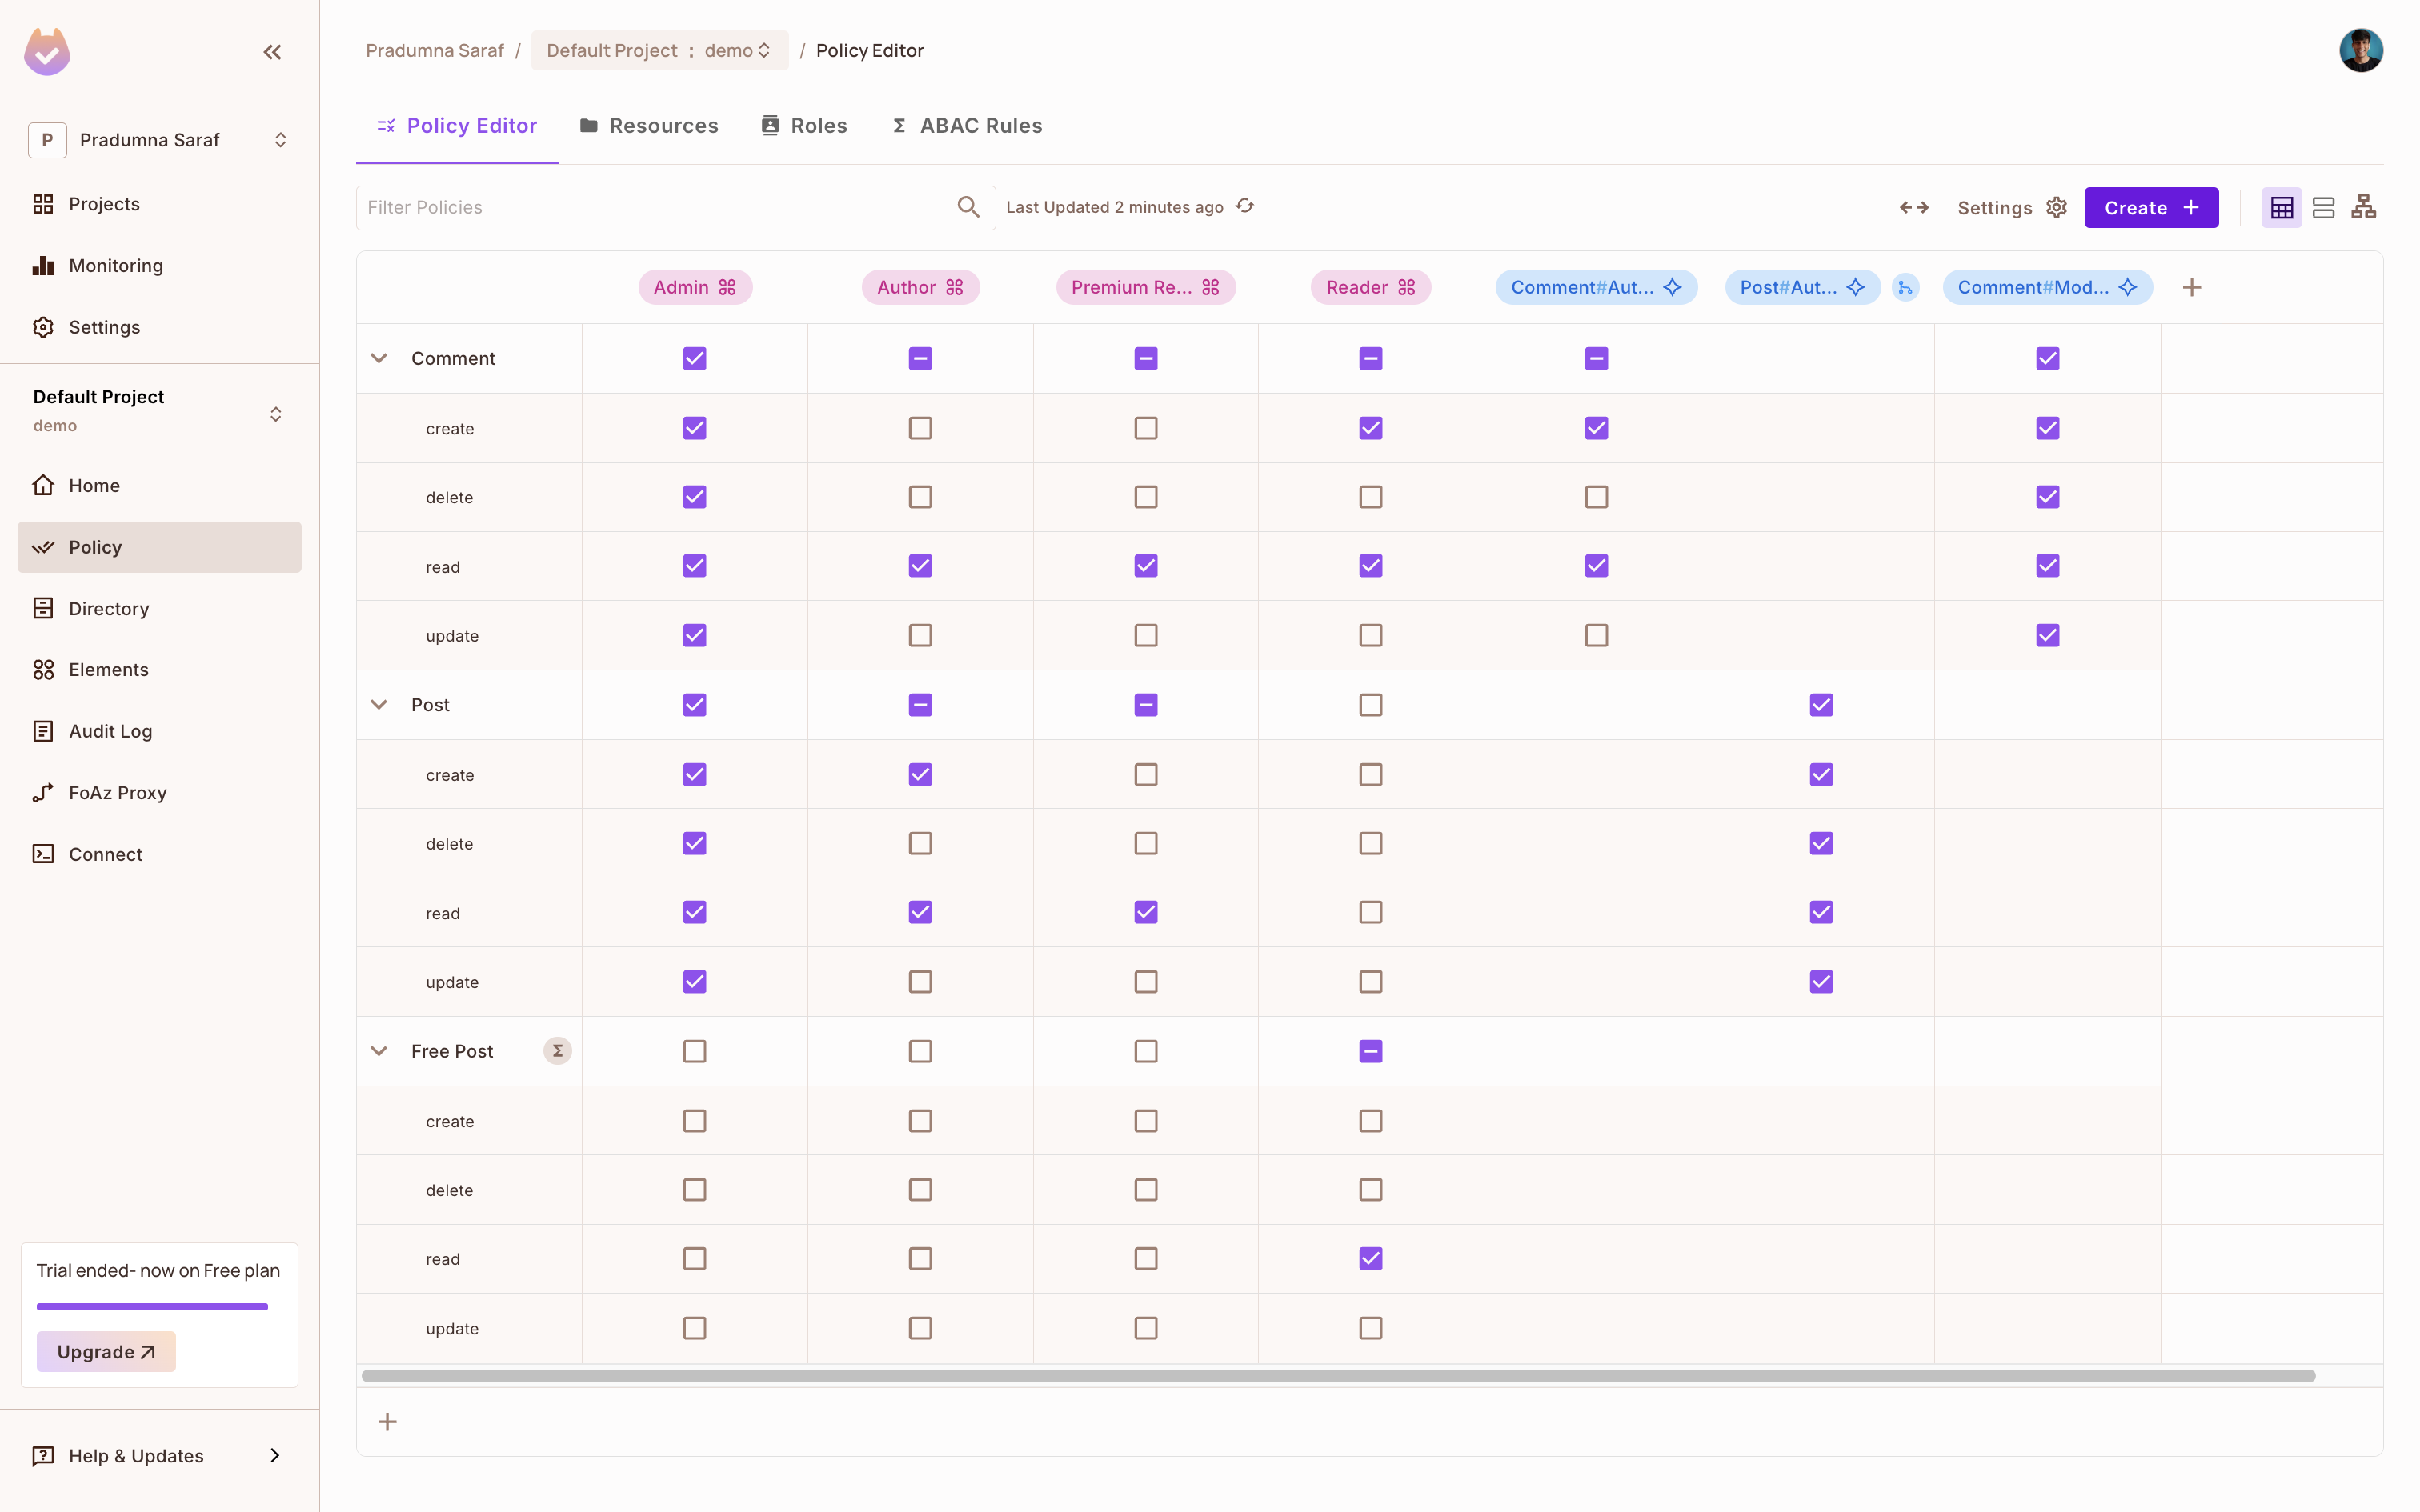
The blogging-platform template creates:
| Policy element | What the template defines |
|---|---|
| Resources | Post (with a premium boolean attribute) and Comment, each with create, read, update, and delete actions |
| Roles | Admin (all actions), Author (create and read posts, read comments), Reader (create and read comments), and Premium Reader (read posts and comments) |
| Relationship | A Post is the parent of its Comment instances. An Author of a post instance becomes a Moderator of the comments on that post. This rule is relationship-based access control (ReBAC). |
| Resource set | Free Post contains posts where premium is false. Readers can read free posts. This rule is attribute-based access control (ABAC). |
This tutorial uses one rule from the policy: the Author role can create a Post, and the Reader role cannot. To change which role can perform an action, check or clear the box in the Policy Editor.
2. Get your API key
Your Express.js app and the PDP authenticate with Permit.io with your environment API key. Copy the API key of the environment where you applied the template. See Get your API key.
Anyone with the environment API key can change that environment's policy through the Permit API. Load the key from an environment variable, and don't commit it.
3. Run the PDP
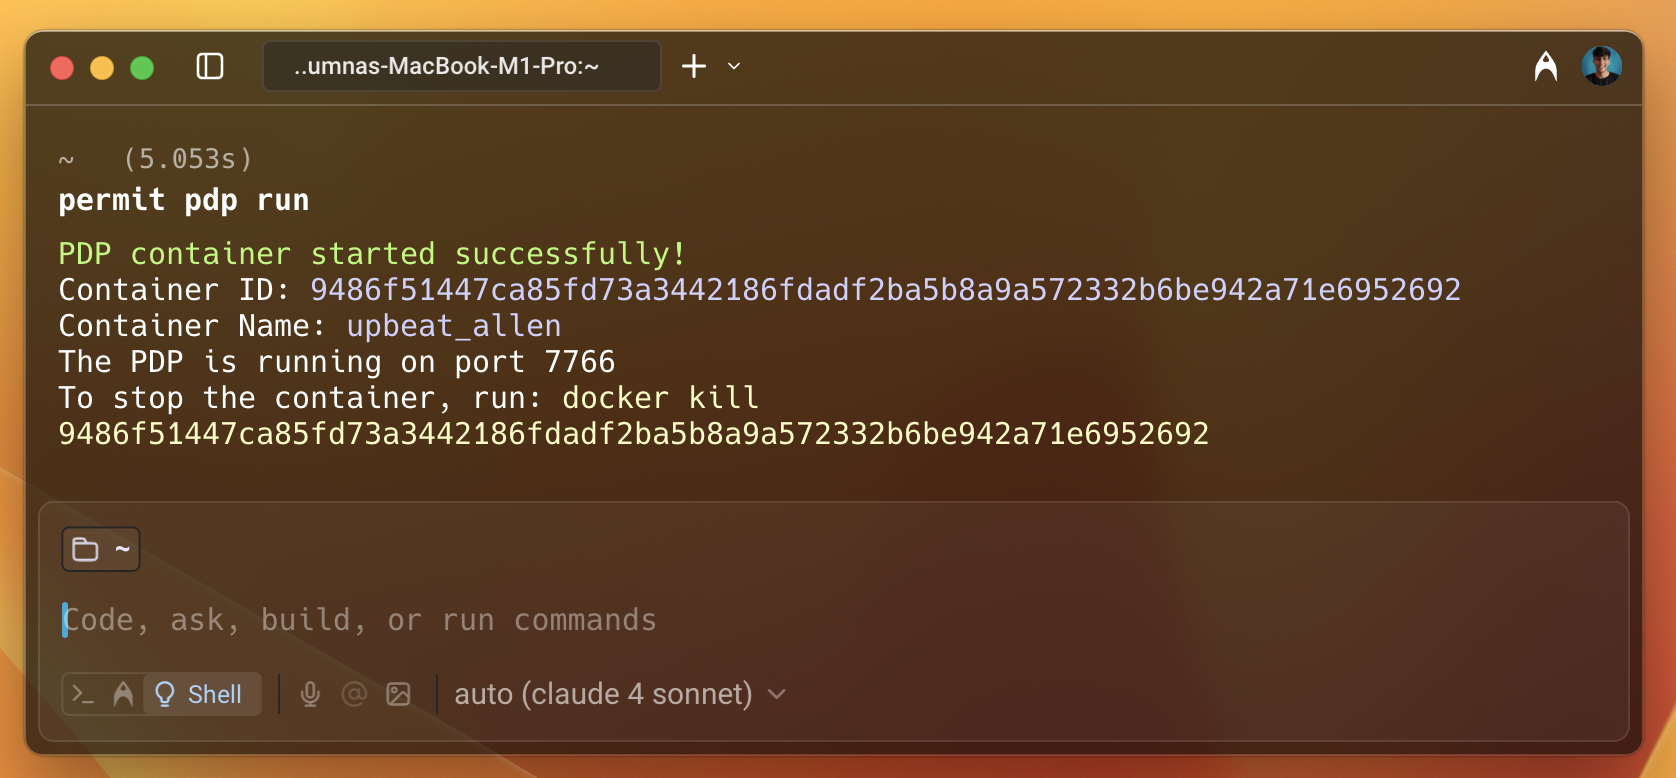
The PDP evaluates each permit.check() call against your policy. Start a PDP container with the Permit CLI:
permit pdp run
The command starts the PDP in Docker and prints the container ID and name. The PDP listens on port 7766, so your app connects to it at http://localhost:7766.
The Free Post resource set is an ABAC rule, and the Cloud PDP doesn't evaluate ABAC rules, so run the container PDP for this policy. To run the container with docker run instead, or to check that the PDP is healthy, see Run the PDP.
4. Build the Express.js app
Install the Node.js SDK
In your Express.js project directory, install the Permit Node.js SDK:
npm install permitio
The code in this tutorial also uses express and body-parser. Install those packages with npm if your project doesn't have them. For all SDK options, see the Node.js SDK quickstart.
Initialize the Permit client in server.js
Create a file named server.js with the following code:
// server.js
const express = require('express');
const bodyParser = require('body-parser');
const { Permit } = require('permitio');

const app = express();
const port = 8000;

app.use(bodyParser.json());

const permit = new Permit({
  token: process.env.PERMIT_API_KEY,
  pdp: process.env.PDP_URL,
});
The code creates an Express.js app on port 8000, parses JSON request bodies with body-parser, and creates a Permit client. The client reads two environment variables:
| Variable | Value |
|---|---|
PERMIT_API_KEY | Your environment API key from 2. Get your API key |
PDP_URL | The PDP address from 3. Run the PDP: http://localhost:7766 |
Add the /register endpoint
Add the following code to server.js. The POST /register handler syncs the user to Permit.io with permit.api.users.sync(), then assigns the user the Reader role in the default tenant.
app.get('/', (req, res) => {
  res.json({ message: 'Hello, Express with Permit!' });
});

// Register a new user
app.post('/register', async (req, res) => {
  const { email, first_name, last_name } = req.body;

  if (!email || !first_name || !last_name) {
    return res.status(400).json({ error: 'Missing required fields' });
  }

  try {
    // Sync user with Permit
    const user = await permit.api.users.sync({
      key: email,
      email,
      first_name,
      last_name,
    });

    // Assign role as part of registration
    const assignedRole = {
      user: email,
      role: 'Reader',
      tenant: 'default'
    };
    const response = await permit.api.users.assignRole(assignedRole);

    // Continue with your app's registration logic
    res.status(201).json({ message: 'User registered and role assigned', user, response });
  } catch (err) {
    console.error('Registration failed:', err);
    res.status(500).json({ error: 'Registration failed' });
  }
});
The user's email address is the user key in Permit.io. Your app passes the same key to permit.check().
Protect the /posts endpoint with permit.check()
Add the following code to server.js. The POST /posts handler asks the PDP whether the user in the request body can create a Post, and returns 403 when the PDP denies the request.
app.post('/posts', async (req, res) => {
  const { user } = req.body;
  const action = 'create';
  const resource = 'Post';

  if (!user) {
    return res.status(400).json({ error: 'Missing required fields' });
  }

  // Check if the user is allowed to create a post
  try {
    const permitted = await permit.check(user, action, resource);
    if (permitted) {
      // ... proceed with creating the post
      res.json({ message: 'You are authorized to create a post' });
    } else {
      res.status(403).json({ message: 'You are not authorized to create a post' });
    }
  } catch (err) {
    console.error('Error creating post:', err);
    res.status(500).json({ error: 'Error creating post' });
  }
});

app.listen(port, () => {
  console.log(`Server listening on http://localhost:${port}`);
});
permit.check() takes the user key, the action, and the resource type, and resolves to true or false. To protect other endpoints, such as commenting or editing, change the action and resource values.
In a production app, take the user key from your authenticated session. This example reads the user key from the request body so that you can test the endpoint with curl.
Start the Express.js app
Set the environment variables and start the app, replacing <YOUR_API_KEY> with your API key:
export PERMIT_API_KEY=<YOUR_API_KEY>
export PDP_URL=http://localhost:7766
node server.js
The app listens on http://localhost:8000.
5. Test the permission check
Register two users, give one of them the Author role, and confirm that the PDP allows only that user to create a post.
Register two users
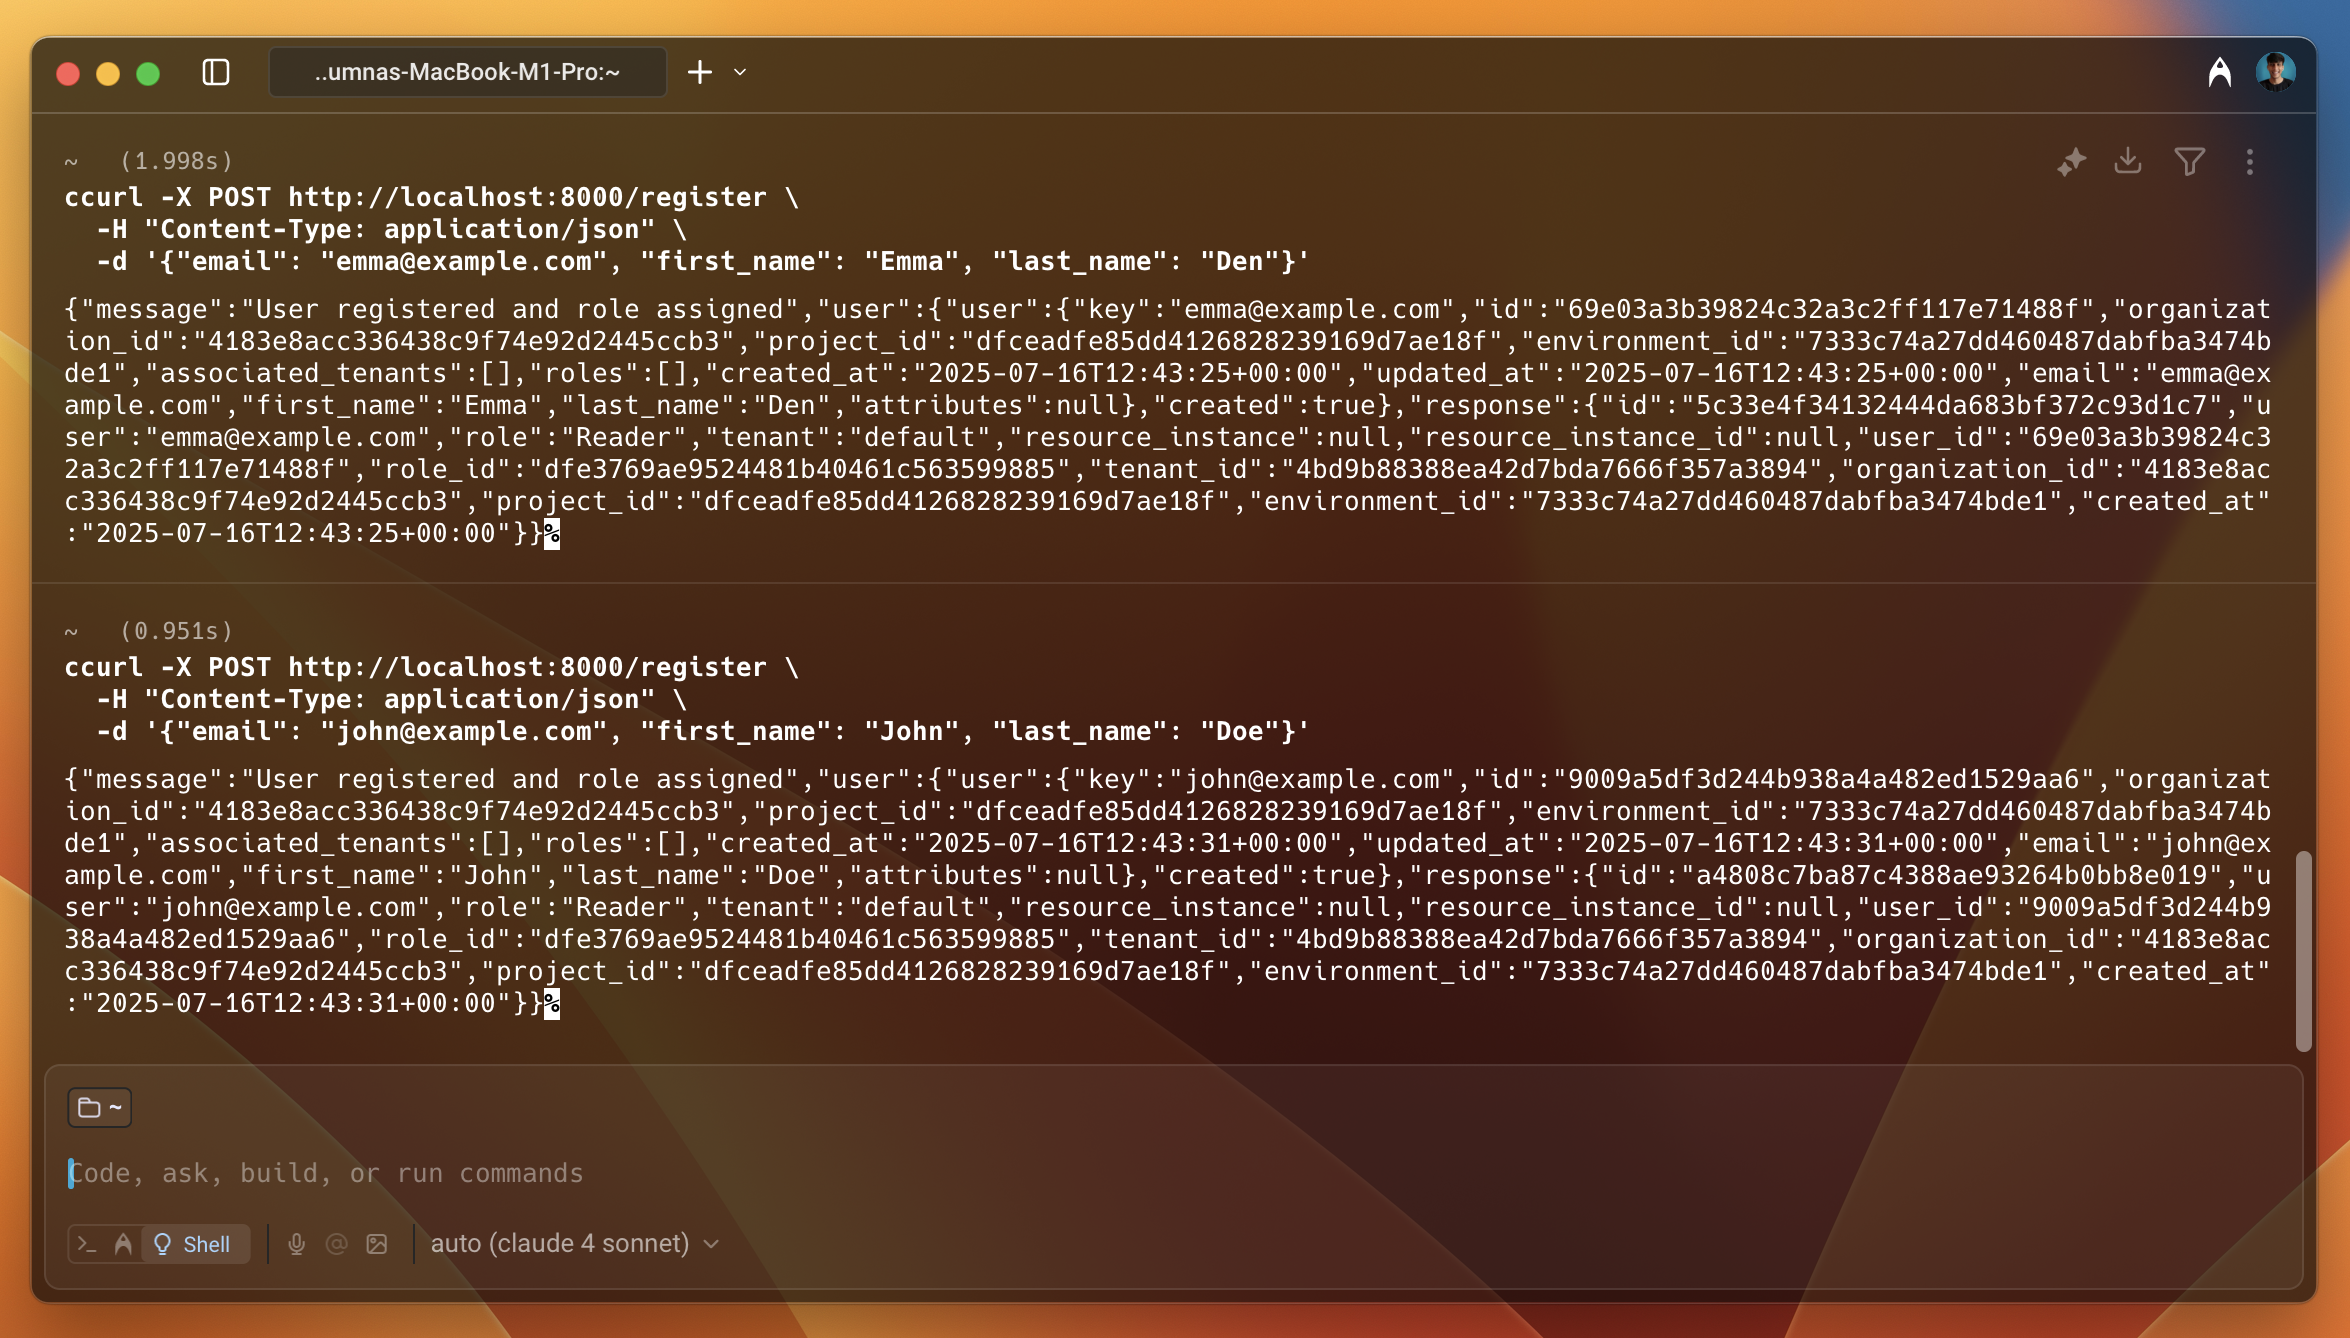
In a second terminal, register John and Emma:
curl -X POST http://localhost:8000/register \
  -H "Content-Type: application/json" \
  -d '{"email": "john@example.com", "first_name": "John", "last_name": "Doe"}'

curl -X POST http://localhost:8000/register \
  -H "Content-Type: application/json" \
  -d '{"email": "emma@example.com", "first_name": "Emma", "last_name": "Den"}'
Each request returns "message": "User registered and role assigned", the synced user under user, and the role assignment under response, with "role": "Reader" and "tenant": "default".
Assign John the Author role
Both users have the Reader role, which can't create posts. Give John the Author role in the Permit dashboard:
- Open the Directory screen and select
john@example.comto open the Edit User panel. - Under Permissions Per Tenant, select the Default Tenant.
- In Top Level Access, add the Author role.
- Click Save.
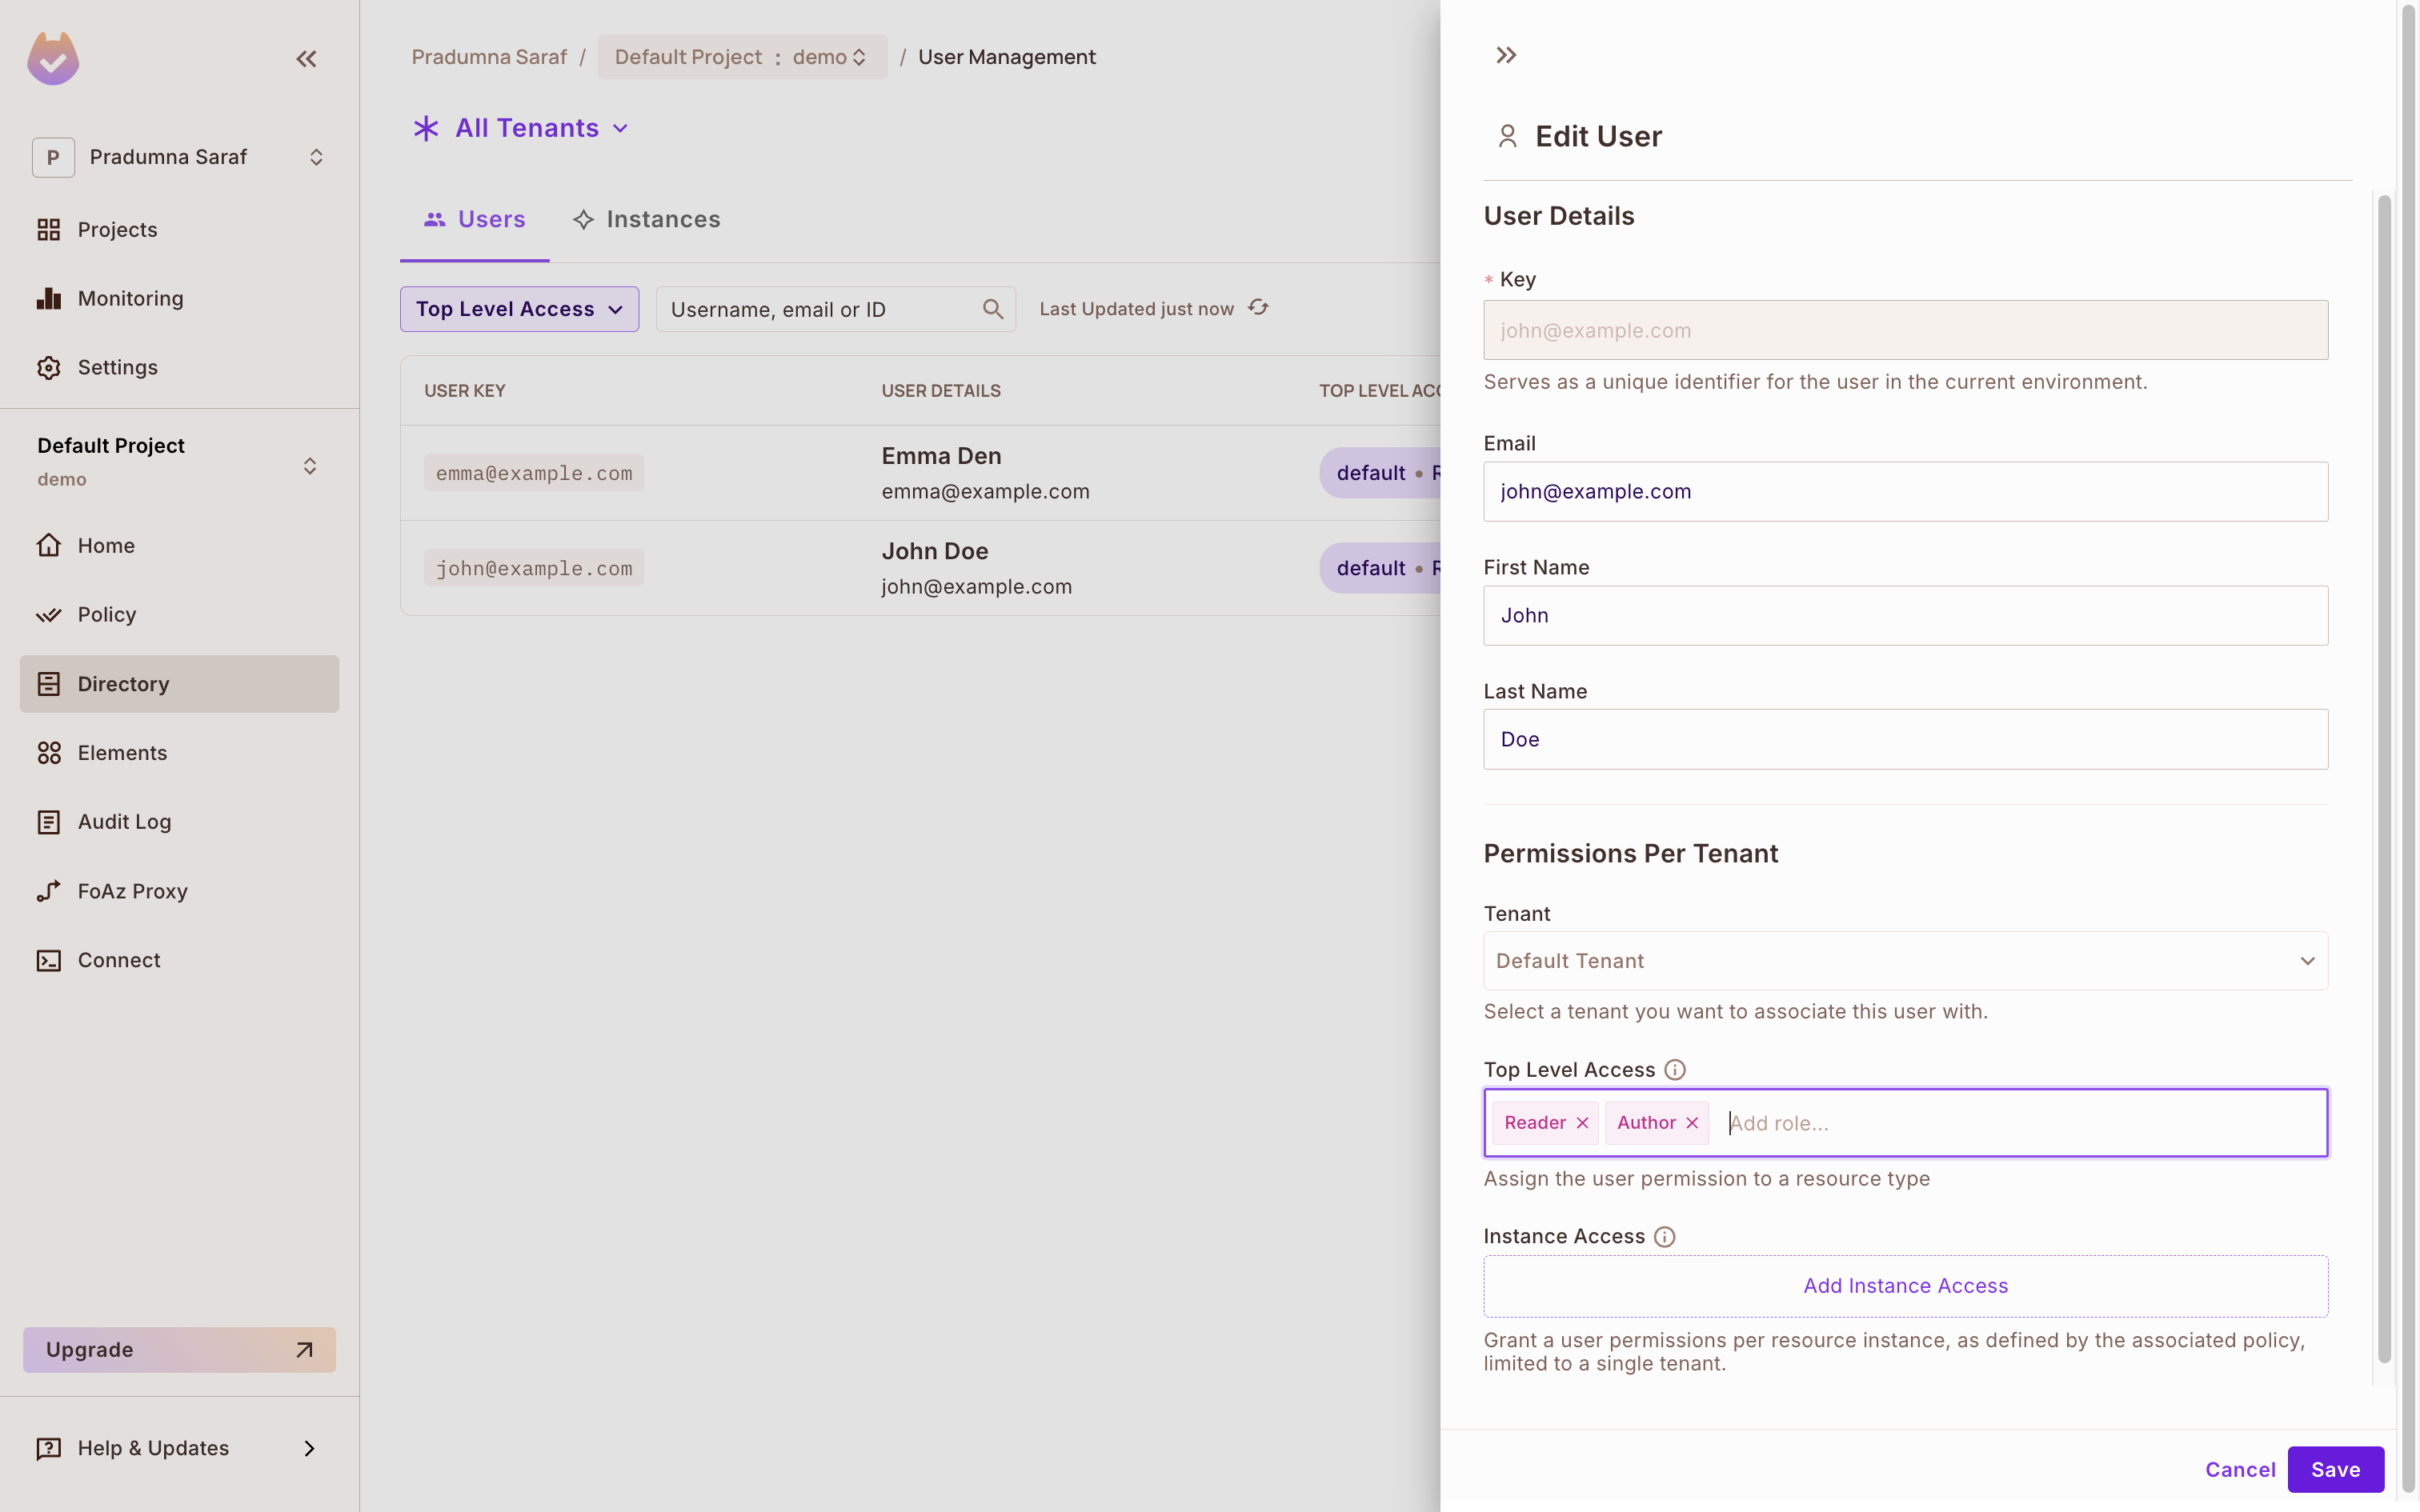
For other ways to assign roles, including the API and SDK, see Sync users.
Check that John can create a post and Emma can't
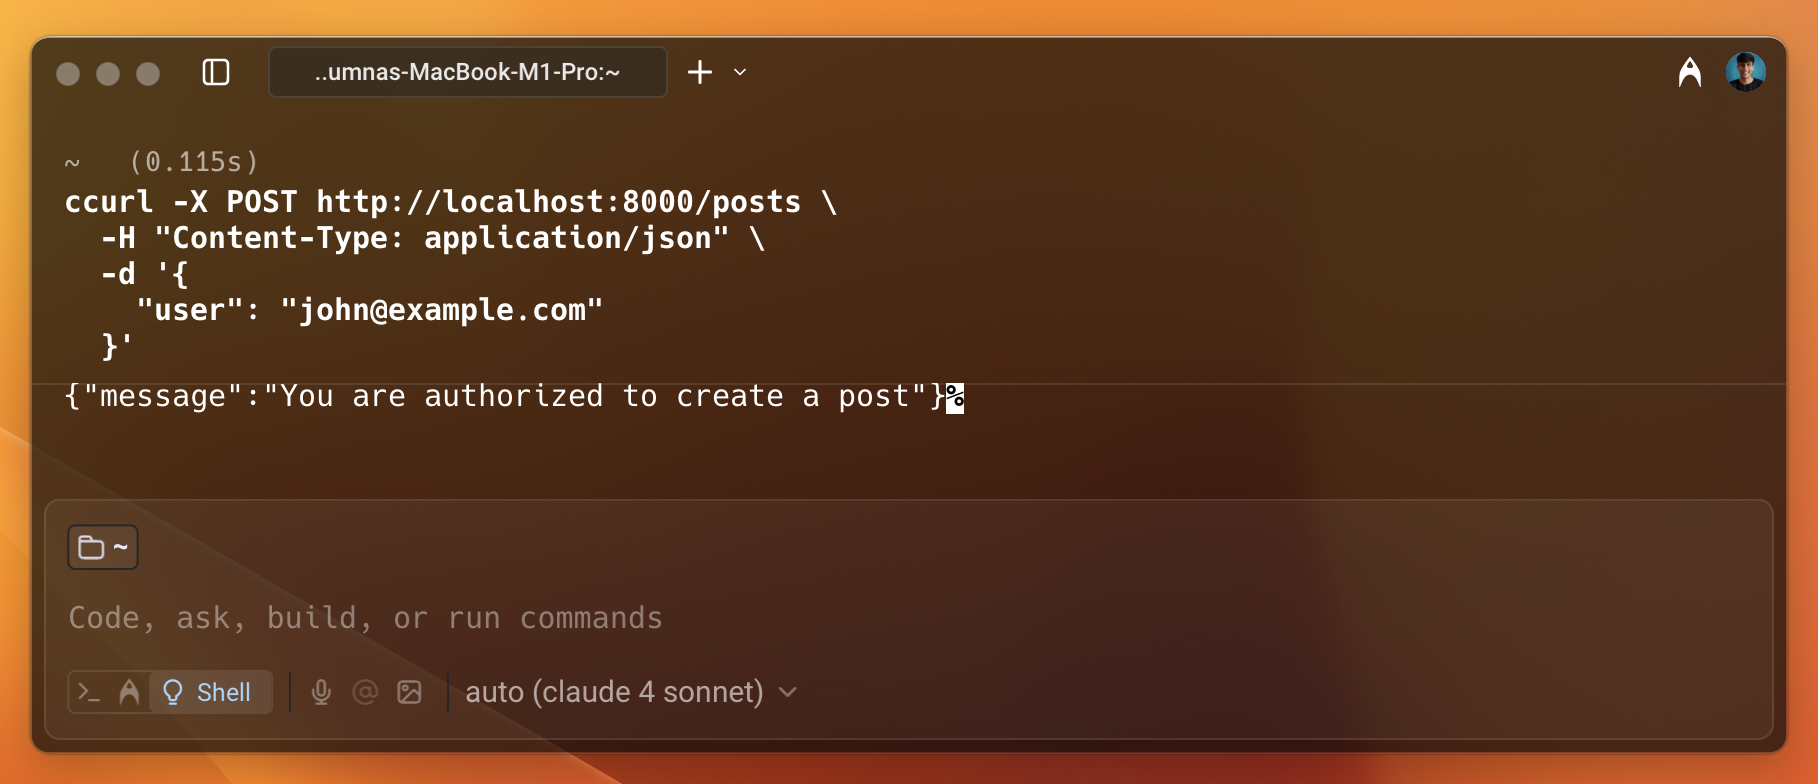
Send a POST /posts request for John:
curl -X POST http://localhost:8000/posts \
  -H "Content-Type: application/json" \
  -d '{"user": "john@example.com"}'
The PDP allows the request because John has the Author role. The app returns {"message":"You are authorized to create a post"}.
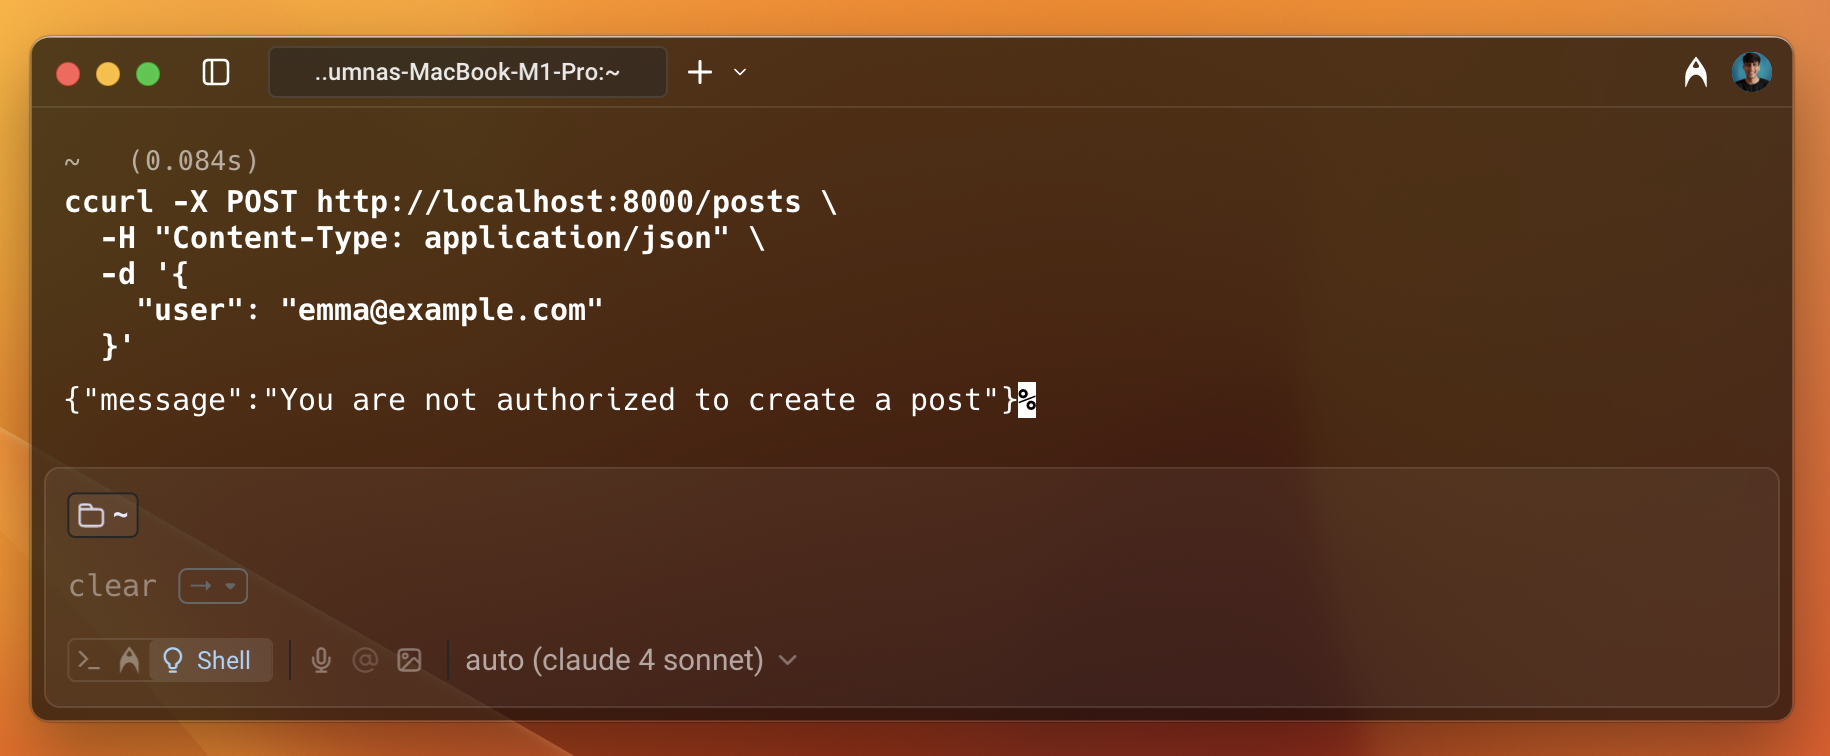
Send the same request for Emma:
curl -X POST http://localhost:8000/posts \
  -H "Content-Type: application/json" \
  -d '{"user": "emma@example.com"}'
The PDP denies the request because Emma has only the Reader role. The app returns HTTP 403 with {"message":"You are not authorized to create a post"}.
Each check also appears in the Audit Log screen of the Permit dashboard, with the user, action, resource, and decision.
Next steps
- Check permissions with the Node.js SDK: SDK installation, configuration, and more
permit.check()examples. - Check permissions with permit.check(): check against tenants, resource instances, and attributes.
- Build RBAC policies: create roles and permissions for your own resources.
- Embed user management with Permit Elements: let your users manage roles from your app.